Vibe App Scanner: Stop Shipping Vulnerabilities Your AI Tool Won’t Warn You About
Your AI coding tool can build a full app in a weekend. What it won’t do is tell you the Supabase table anyone can read, the service-role key sitting in your frontend code, or the API that trusts whatever user ID it’s handed. Those aren’t hypothetical — they’re the exact mistakes security auditors keep finding in vibe-coded apps.
Vibe App Scanner checks your live app the way a real attacker would, then hands you the fix — not just the warning.
What does it actually do?
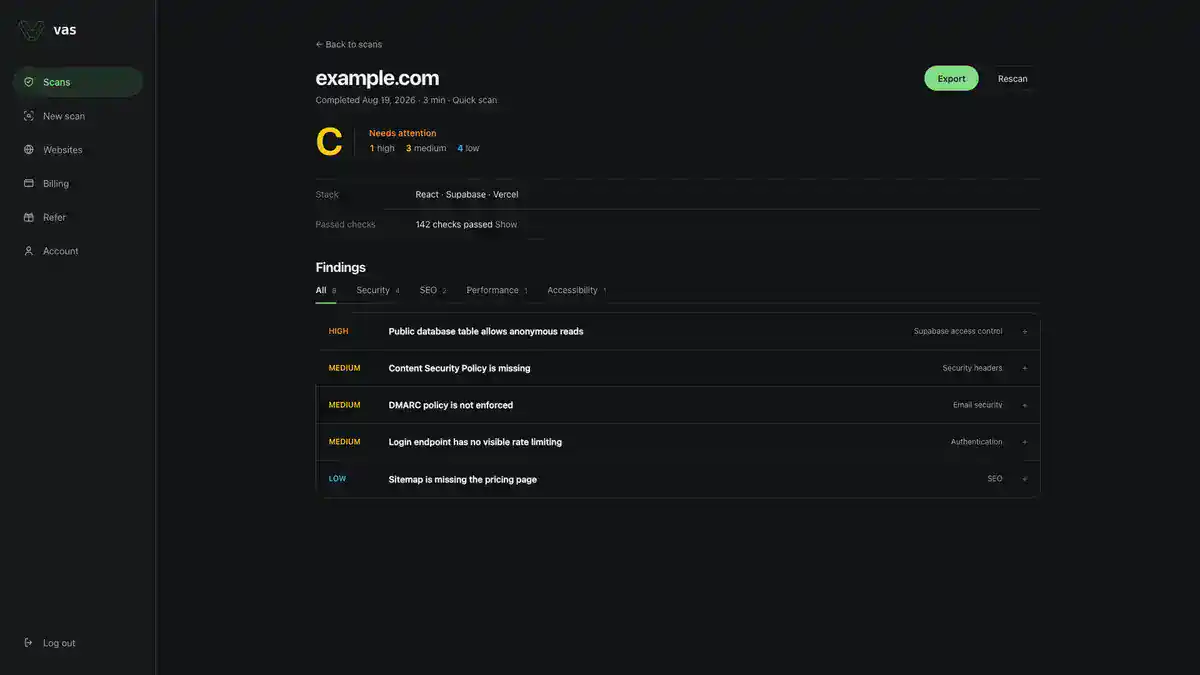
Just enter your app’s URL and Vibe App Scanner auto-detects your stack — React, Supabase, Vercel, and 20+ platforms — then runs 150+ targeted checks tuned specifically for the vulnerabilities AI coding tools most commonly introduce. Add login credentials and it tests authenticated flows too, catching access-control issues that only show up once someone’s signed in.
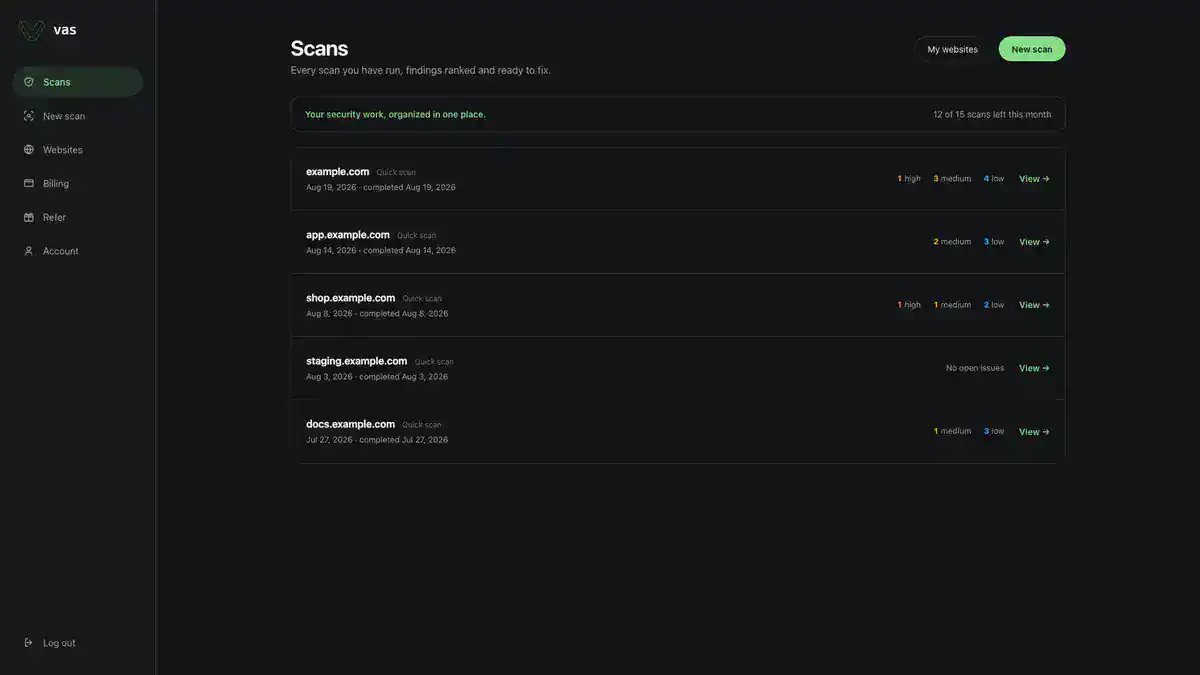
See what actually matters, skip the noise
Every finding gets ranked by severity, so you fix what would actually get you breached first instead of wading through low-priority clutter. Each issue comes with a plain-English explanation of why it’s dangerous — not just a CVE number nobody has time to look up.
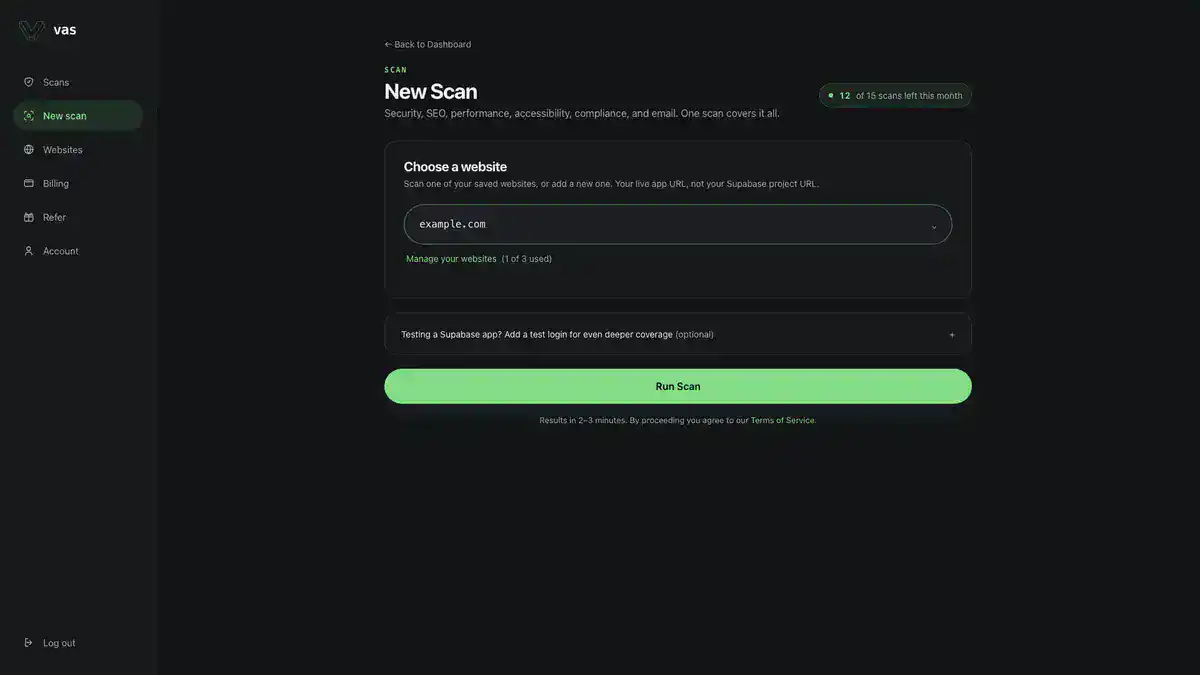
Fix it without guessing
This is where it earns its price: every finding ships with copy-paste remediation code you can hand straight to Cursor, Claude Code, Lovable, or your developer. Review the raw evidence behind each flag, apply the fix, scan again, confirm it’s gone.
Who is this for?
Built for developers, solopreneurs, and agencies shipping apps with AI coding tools — especially anyone without a security engineer double-checking every deploy.